Background
- The community runs a Kubernetes cluster with GitOps, hosting 36 applications: Argo CD manages deployment, Cilium enforces network policy, OpenBao with External Secrets manages secrets, CloudNativePG and Longhorn handle data and backups, and there is full metrics, logs, and traces observability.
- I take part in cluster design and day-to-day releases, and lead development of the services below.
Zero-trust secret bootstrap for production
- Problem: When the identity and review core service first went to production, it needed a temporary Keycloak administrator and a set of service secrets, without leaving any long-lived privileged credentials behind.
- Approach: A controller generates secrets and writes them to OpenBao, and workloads only read the Secrets synced back; Argo CD sync-waves and hooks fix the order—create Keycloak, run a temporary reconciler, harden the configuration, create and verify the real administrator—and only when everything passes is the temporary administrator deleted, stopping at any failed step.
- Result: No temporary privileged account remains in production, and the full secret lifecycle is documented.
Production accepts only versioned images
- Problem: While a CI runner was broken, production temporarily accepted images tagged latest, making deployments untraceable.
- Approach: Wrote a plan document first, then implemented a dependency-free checker test-first and wired it into CI.
- Result: Production images must use a SemVer version (optionally with a digest), and non-compliant manifests cannot be merged.
Services I lead
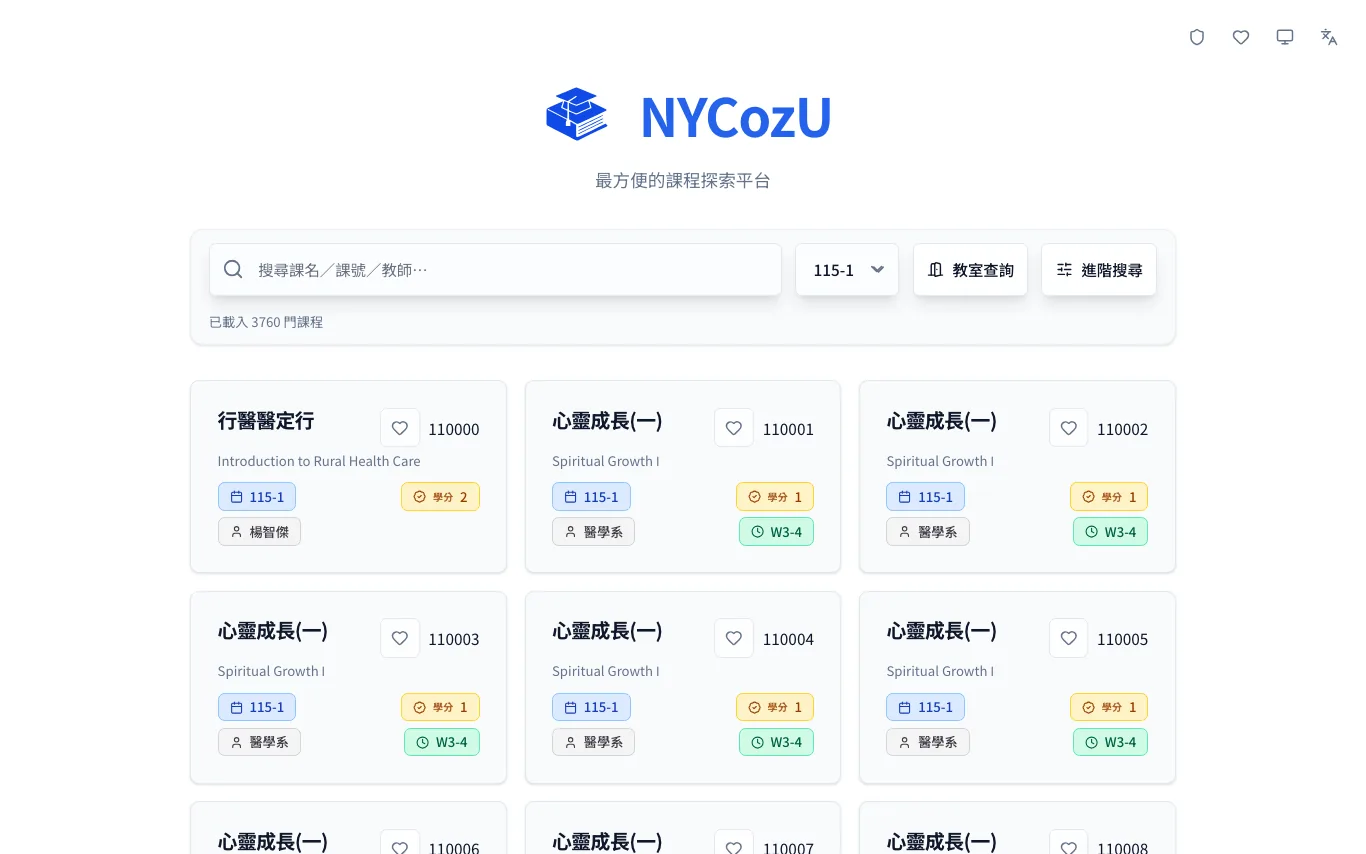
- coz-planner: An NYCU course-search site I founded, built with Go (Gin, GORM) and SvelteKit, with a self-implemented OAuth authorization server (PKCE) and MCP tools; it syncs timetables through the university's OAuth, filters courses, and exports ICS/CSV.
- Core System: The community's identity and review core. I implemented FXP from scratch so approved programs run as Kubernetes Jobs with federated workload identity, and completed two rounds of security fixes and RBAC hardening.
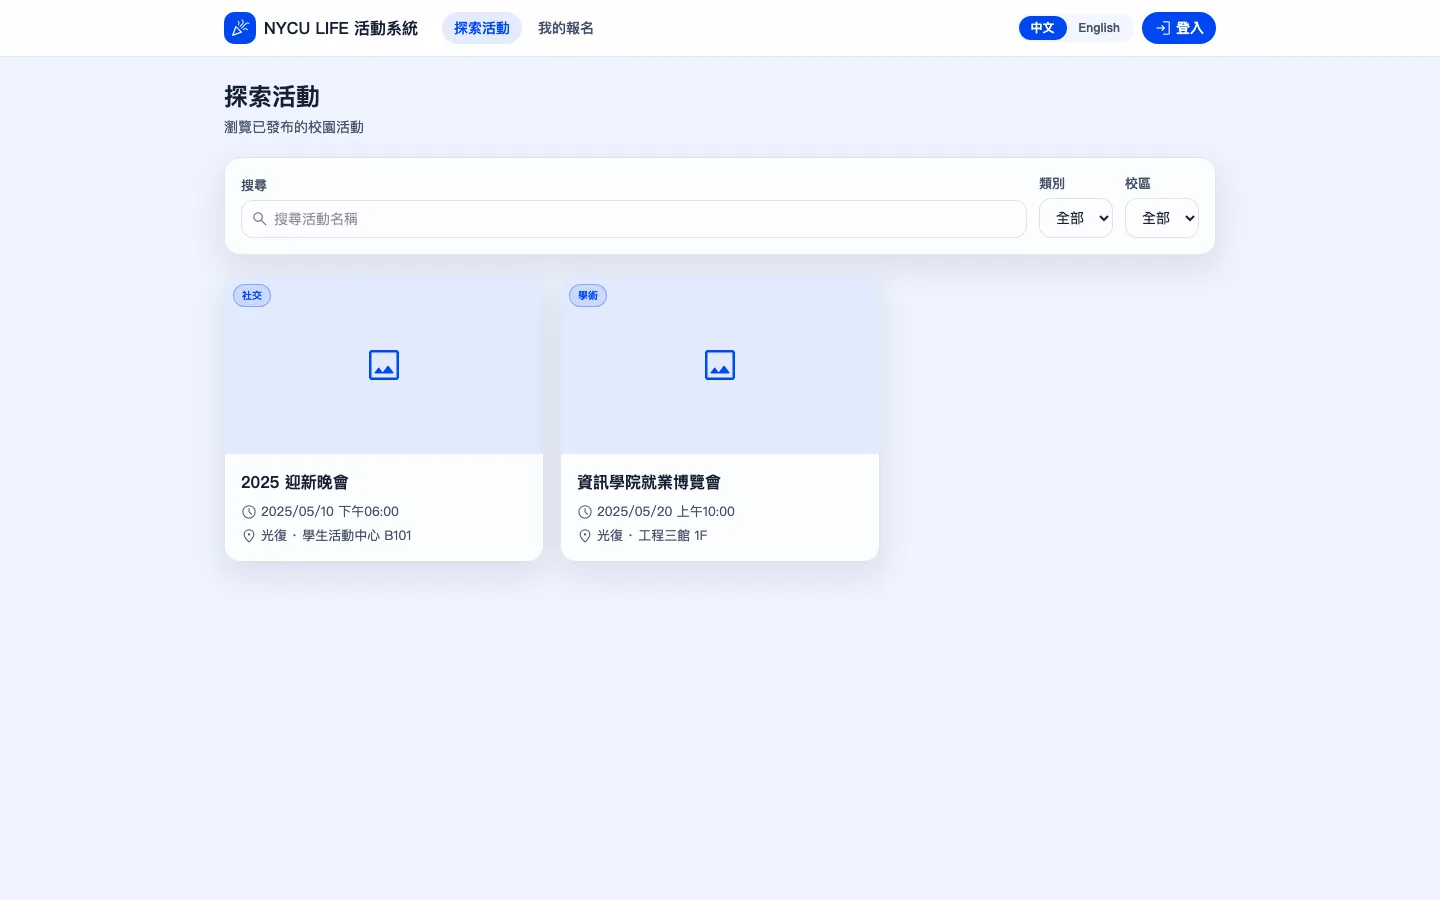
- Events: A campus event system. I led the UI overhaul, fixed the NYCU OAuth token exchange, hardened production sessions, and built the survey feature.
Screenshot provenance: Product screenshots from the NYCU LIFE official site.